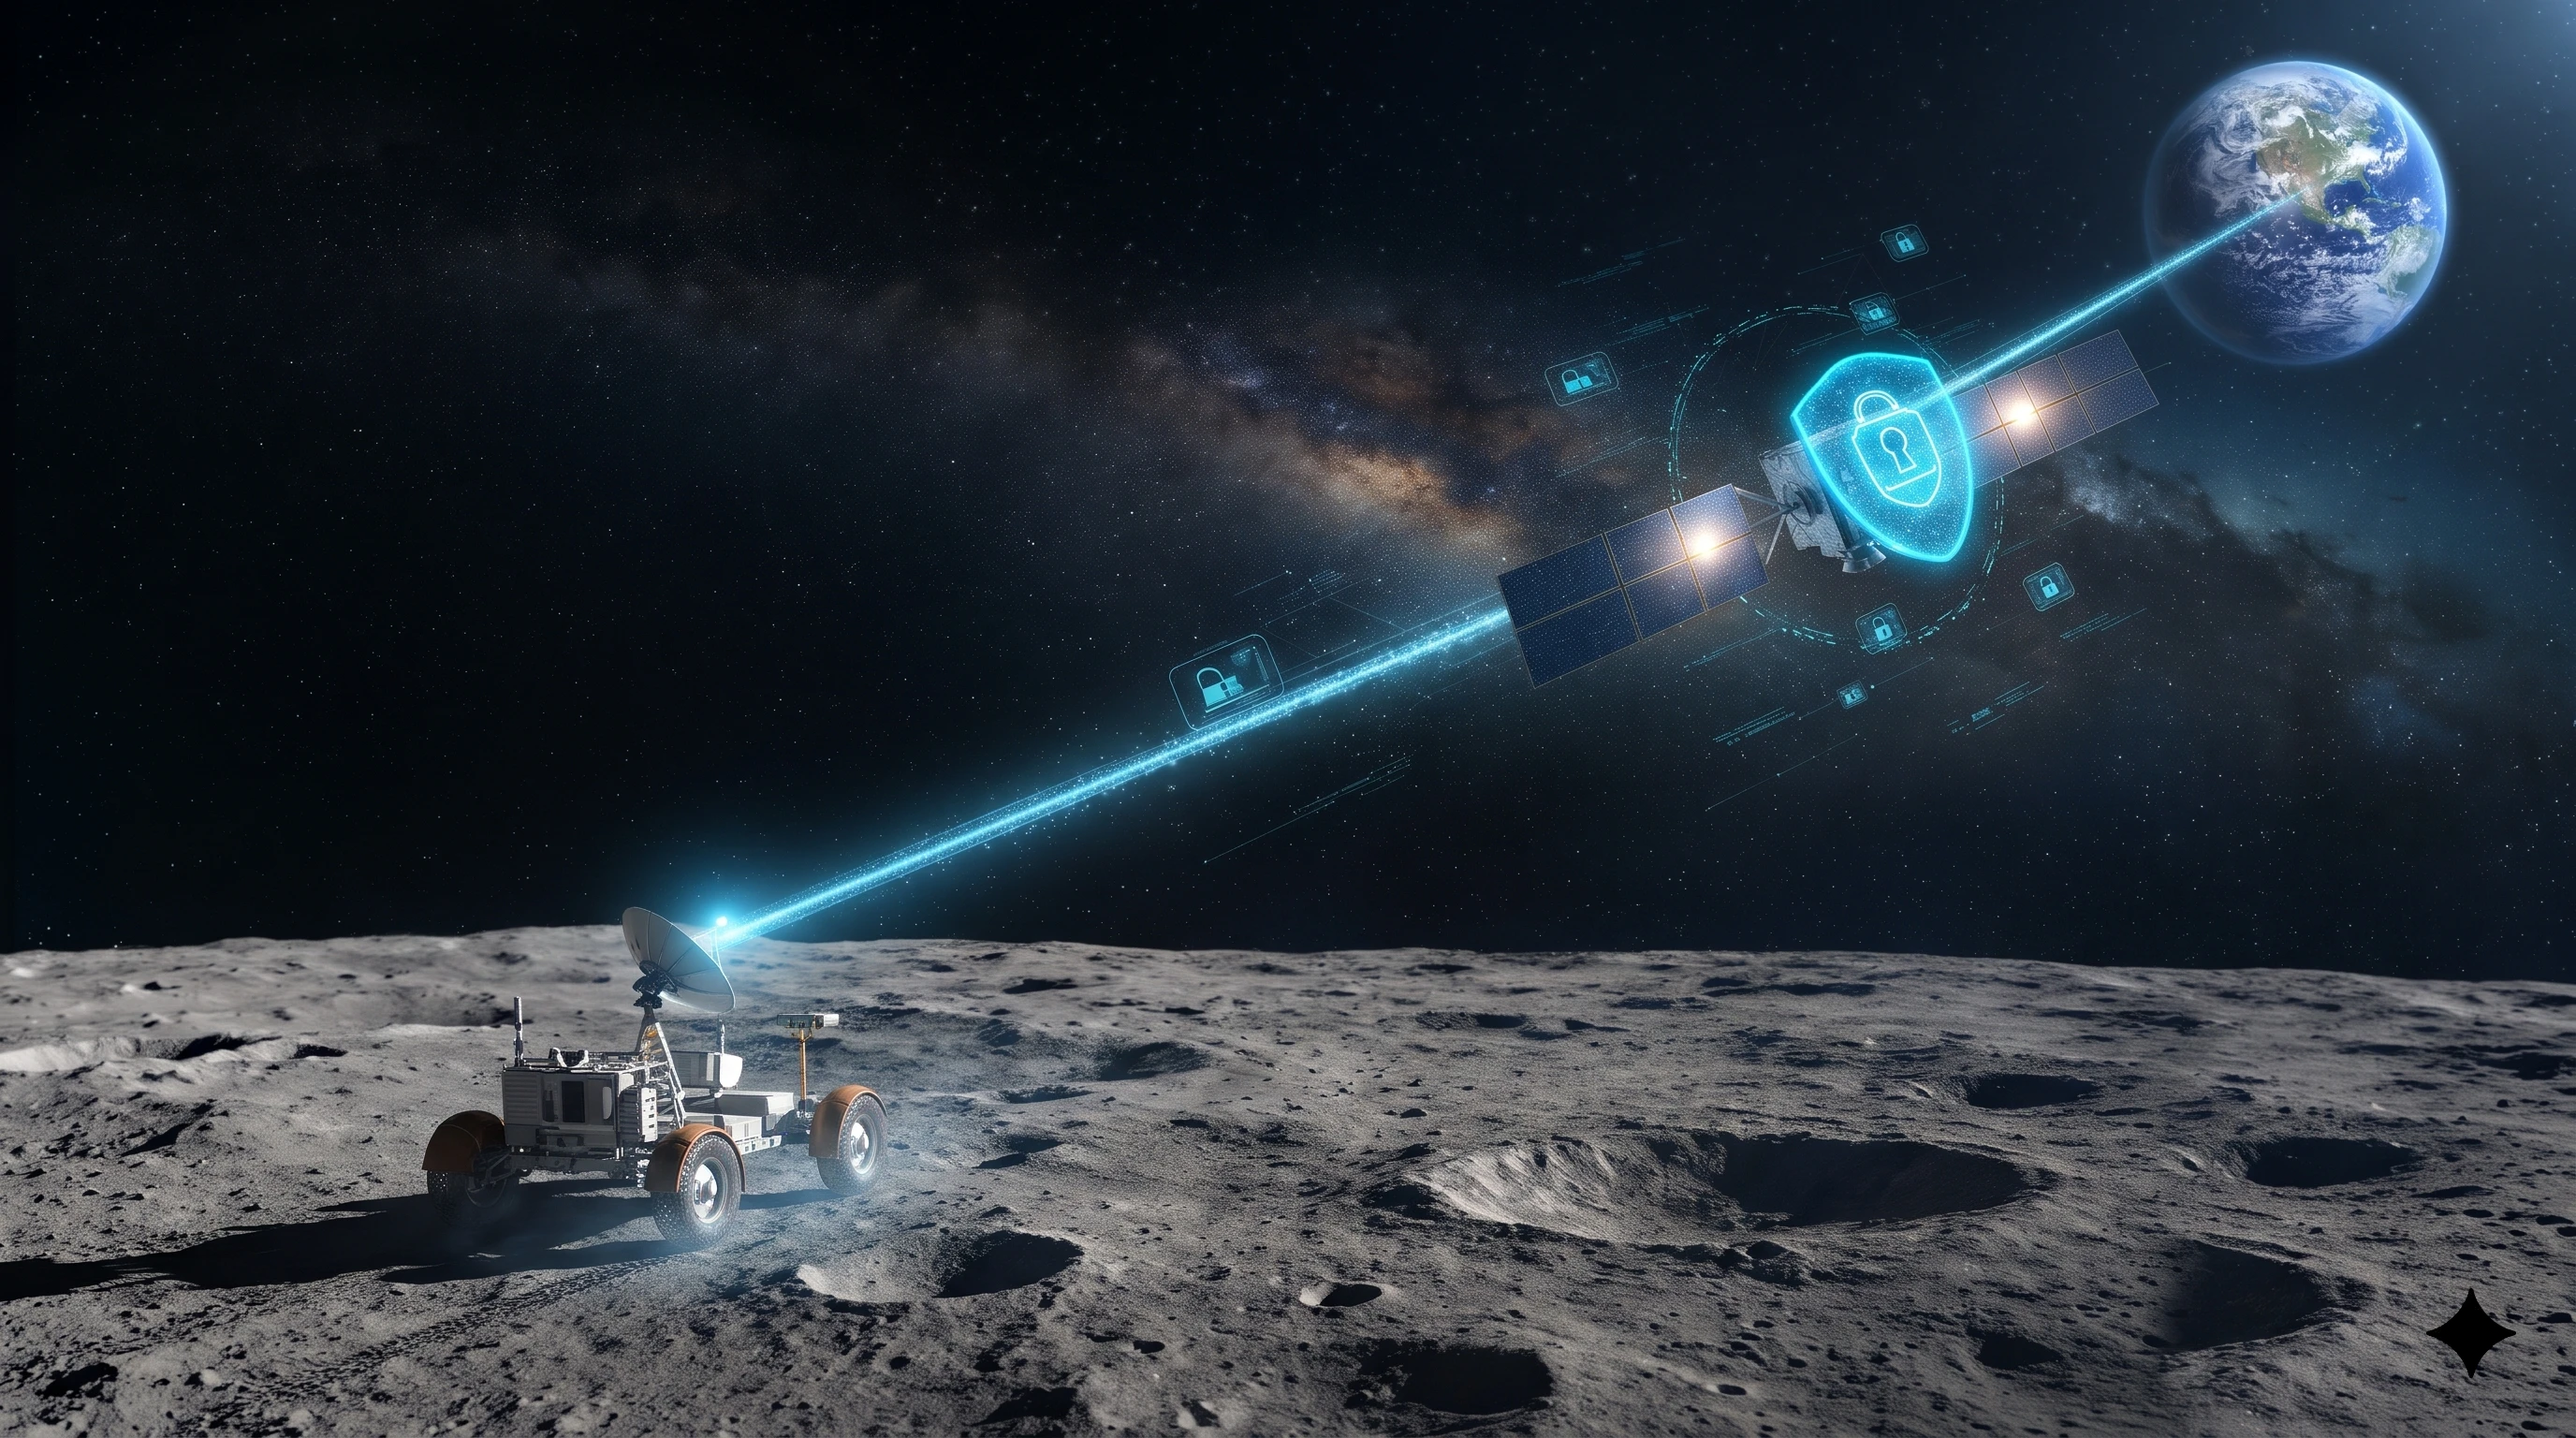
As Europe prepares for sustained robotic exploration of the Moon and beyond, the communication infrastructure of future missions is shifting towards Delay-Tolerant Networking (DTN). DTN and its core Bundle Protocol (BP) are designed to support reliable data exchange across networks with high propagation delays and intermittent connectivity, as they will occur in lunar and deep-space operations. To make such networks usable for multiple operators, the security of the exchanged data must be guaranteed on a standardised basis. The central element of this standardisation effort is Bundle Protocol Security (BPSec), which allows bundles to be protected at block level: a Block Confidentiality Block encrypts the bundle data, while a Block Integrity Block authenticates it, so that payloads remain private and verifiable even when they pass through relays operated by other parties.
The activity targets a comprehensive, interoperable and standards-compliant implementation of BPSec on top of the current Bundle Protocol version 7. The resulting module shall cover the generation, verification, forwarding and reception of bundles, a configurable security policy engine, and the convergence layer interfaces required to transport bundles over different physical links.

A major technical challenge of the project is key management. The BPSec standard defines how security blocks are structured and how security contexts select cryptographic parameters, but it does not define how keys are established, identified or revoked between two nodes. Without a sound key management concept, even a cryptographically strong module would leave the network as a whole exposed. The consortium will therefore develop a holistic key management concept covering all three levels that a key touches in a mission: the operational level on the ground, from key generation through lifecycle management to upload to the spacecraft; the network level, where keys must be deployed and exchanged securely between nodes; and the local level on the device, where secure storage and recovery from corrupted key material directly affect the reliability of the spacecraft. Several candidate strategies will be specified. The most appropriate strategies will be implemented in a dedicated key management component of the module and documented in a draft CCSDS Orange Book on BPSec key management, making the results available to the wider space standards community.
To validate the module under realistic conditions, the consortium will extend an existing network simulator into a dedicated test bench. The simulator will host simulated nodes running the BPSec implementation, compute line-of-sight communication windows from orbit simulations, and allow configurable link conditions such as latency, bandwidth limits, packet loss and link disruptions, as well as hardware-in-the-loop integration of physical nodes. This environment will be used to evaluate the secure end-to-end data transmission of the module in representative mission scenarios, using the ArgoNET lunar network mission and the ESA Moonlight programme as the leading use case.
SANCTUARY Systems GmbH is the prime contractor, working with DSI Aerospace and Airbus Defence and Space in this activity, which started in January 2026 and is expected to end in February 2029.
by Emmanuel Stapf