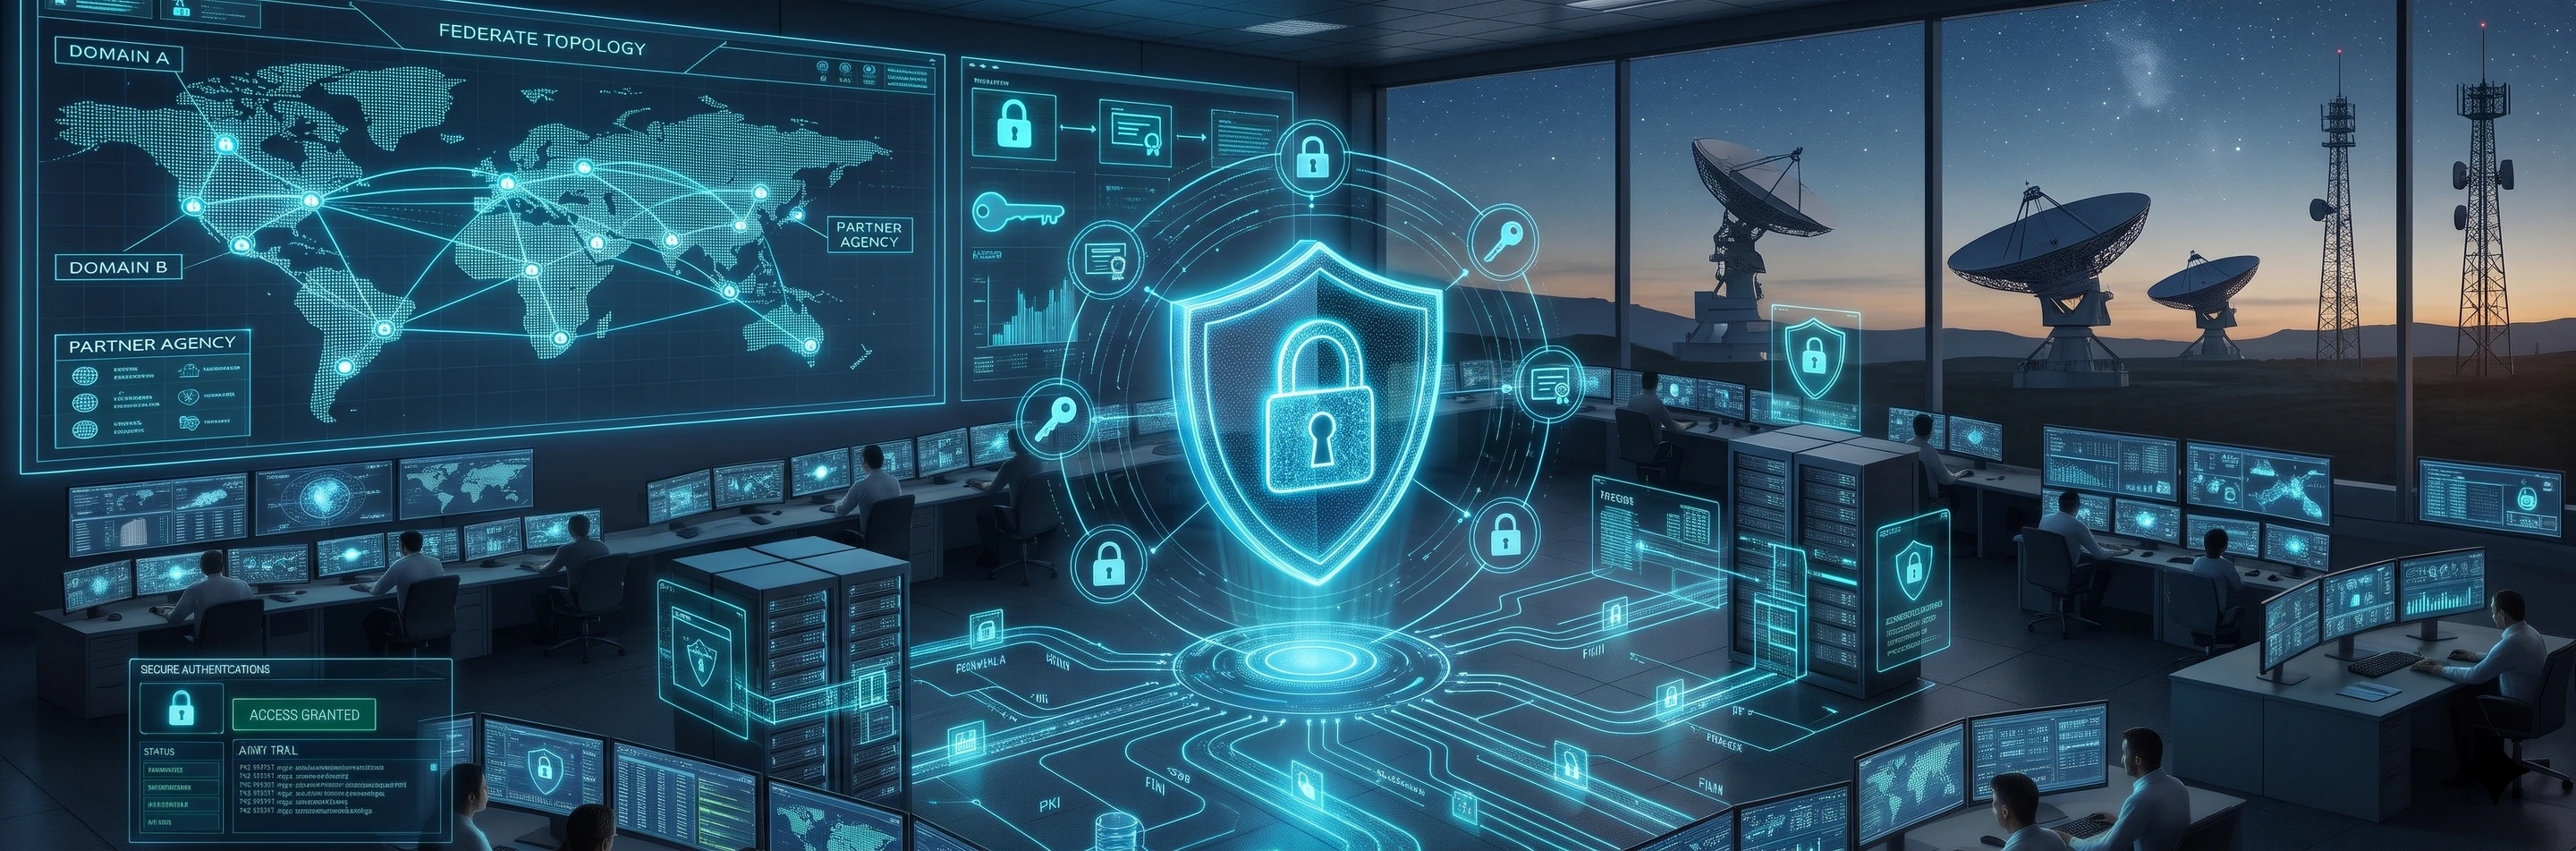
In response to the increasing number of collaborative space missions, in which multiple agencies, companies and research institutions jointly operate spacecraft and ground infrastructure, this activity addresses the challenge of secure, cross-organisational access to distributed mission operations services. As space missions carry payloads of independent stakeholders and ground segments migrate to cloud-native, multi-site architectures, the traditional security model — in which all components sit inside a single trusted perimeter — is no longer sufficient. In a federated system, the overall security posture is determined by the weakest participating policy. The activity therefore defines security architectures for distributed mission ground segments based on federated identity and access management and validates them in a dedicated testbed.
At the core of the solution is a federated Public Key Infrastructure (PKI), in which the PKIs of the participating organisations are interconnected through a bridge certification authority in line with the CCSDS Intergovernmental Certification Authority (IGCA) concept. This trust backbone allows systems of different organisations to authenticate each other and to verify the authenticity and integrity of exchanged data. On top of it, the activity defines Federated Identity Management (FIM) and Federated Access Management (FAM): users and services authenticate across organisations using the credentials of their home organisation, while the policies governing access decisions are coordinated across the federation through policy-as-code, with each domain retaining control over its own identities, roles and permissions.

The candidate architecture is organised around an Identity Broker that federates the identity providers of the individual organisations and supplies identity and access decisions to the mission applications, which integrate an access control component and communicate through a service mesh with mutual TLS. The architecture follows Zero Trust principles, building on the ESA ZTAMGS project, and is deliberately aligned with open standards and open-source components to remain extensible and avoid vendor lock-in. A particular design challenge is reconciling two protection goals that are in tension in federated environments: non-repudiation, which requires tamper-proof audit logs linking every action to a responsible user, and user privacy, which demands undetectability and unlinkability of actions. The proposed design meets both by restricting access to audit information to authorised auditors only.
To validate the concepts, the consortium will implement a security testbed that instantiates a distributed mission ground segment across multiple organisational domains, comprising mission control, mission planning and simulation systems interconnected by the federated security components. It will be exercised with representative use cases, such as a lunar lander and rover operated by two different entities, in which the rover's telecommands pass through the other entity's ground infrastructure and must be protected end-to-end in encrypted form. The results will inform the required adaptations of existing standards, including potential contributions to CCSDS standardization.
Telespazio Germany GmbH, as the prime contractor, is collaborating with SANCTUARY in this activity, which started in December 2025 and is expected to end in January 2027.
by Ferdinand Brasser